Hejto.pl
Dodaj post

Wpisz coś do wyszukania (minimum 2 znaki)

#informatyka

Fenomen

w Hydepark

4piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.06.09.md

Using Tracealyzer for Embedded Systems Analysis - https://mcuoneclipse.com/2026/06/06/usingtracealyzerforembeddedsystemsanalysis/

The Practitioner’s Guide to AI-Enhanced Hacking - https://www.caido.io/blog/2026-03-24-ai-enhanced-hacking/

The (Anti-)EDR Compendium - https://blog.deeb.ch/posts/how-edr-works/

Powering up a module from the IBM 604: an electronic calculator from 1948 - https://www.righto.com/2026/06/ibm-604-thyraton-tube-module.html

Shellcode Loaders: Advanced Execution & Evasion Tradecraft - https://0xdbgman.github.io/posts/shellcode-loaders-the-art-of-execution/

Koneser

w Hydepark

5piorunów

Mam problem z zasilaczem od komputera, ale nie wiem czy to jest kwestia samego zasilacza. Wydaje identyczne dźwięki jak na tym filmie www.youtube.com/shorts/wS4vaZ-4z1Y Jak na razie zauważyłem to tylko podczas gry w Doom The Dark Ages, dźwięk nasila się gdy wejdę do menu opcji graficznych. Dźwięk jest nieregularnym, czasem występuje częściej, czasem mniej. Wszystkie ustawienia na max oprócz path tracingu, vsync włączony, czyli zablokowane na 60 k/s. Nie uświadczyłem tego dźwięku nigdzie indziej nawet na maksymalnym obciążeniu pc w programie HWiNFO64.

Pod filmem jest komentarz: "W dziale pomocy technicznej powiedziano mi, że ten dźwięk wynika z przejścia między niskim a średnim obciążeniem. Wymieniłem już urządzenie raz, ale sytuacja się nie zmieniła. ...to w pewnym sensie wiąże się też z instalacją elektryczną w moim domu."

I tu pojawia się kolejna kwestia, około 2 lata temu miałem podobne problemy z zasilaczem w innym komputerze, dźwięk aktywował się losowo, intensyfikował pod dużym obciążeniem. Wymieniłem go, problem zniknął.

Czy to faktycznie może być problem instalacji elektrycznej w domu? Jak rozwiązać ten problem?

Mój sprzęt:

* Zasilacz: FSP 1350W

* Procesor: Ryzen 9 9900X

* Karta graficzna: RX 9070 XT

Lider0piorunów

@PurpleJago a przestaw ten guziczek ECO w drugie położenie i zobacz co będzie

Lider0piorunów

@PurpleJago tylko przy wymianie zasilacza modularnego pamiętaj, że te jebane kabelki fizycznie pasują do innych zasilaczy, ale elektrycznie najprawdopodobniej nie i spalisz sprzęt jak pomieszasz

Pokaż więcej komentarzy (17)

GURU

w Ciekawostki

35piorunów

7 czerwca:

* Ogólnopolski Dzień Cyrku bez Zwierząt

* Dzień Informatyka

* Światowy Dzień Oceanów

* Światowy Dzień Guza Mózgu

Osobistość11piorunów

7 czerwca? Dziś jest 8

Pokaż więcej komentarzy (10)

Fenomen

w Hydepark

2piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.06.08.md

Implementing Impacket's Newest Protocol: MS-RAA https://www.abdulmhsblog.com/posts/developingwith-impacket/

Arbitrary Kernel Address Increment via NtQuerySystemInformation https://pwn2nimron.com/blog

Obfuscation vs the Optimizer: An LLVM Middle-End Arms Race https://blog.quarkslab.com/obfuscation-vs-the-optimizer-an-llvm-middle-end-arms-race.html

ThinkPads From the Inside: A Reproducible Path From Archived BIOS to Named SoC Pads https://tetdrad0n.codeberg.page/thinkpad-fw-analysis/

SSD Advisory – How MiraclePtr Crushed Two Sandbox Escapes https://ssd-disclosure.com/ssd-advisory-miracleptr-sandbox/

Fenomen

w Hydepark

6piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.06.05.md

The Newest Instagram "Exploit" is the Goofiest I've Seen - https://www.0xsid.com/blog/meta-account-takeover-fiasco

The Phishy GitHub Issue Case - https://blog.atsika.ninja/posts/the-phishy-github-issue-case/

A four-byte type, an eight-byte stride, one root shell - https://fatgid.io/

The 9.3 Critical Vulnerability Microsoft Dismissed: A Dependency Confusion Story - https://www.wahidfayad.com/blog.html?post=microsoft-dependency-confusion

AI-FI: Reproducing adb to root on Google's TV Streamer using Claude in less than 15 minutes - https://raelize.com/blog/ai-fi-reproducing-adb-to-root-on-googles-tv-streamer-using-claude/

Fenomen

w Hydepark

4piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.06.03.md

How to Deploy a Wii Pwn Challenge - https://towerofhanoi.it/blog/2025-07-20-forsaken-tower-deployment/

Uncovering Hidden Forensic Evidence in Windows: The Mystery of AutoLogger-Diagtrack-Listener.etl - https://www.fortinet.com/blog/threat-research/uncovering-hidden-forensic-evidence-in-windows-mystery-of-autologger

Kernel Karnage – Part 1 - https://blog.nviso.eu/2021/10/21/kernel-karnage-part-1/

Revisiting Two-Shot Kernel Shellcode Execution From Control Flow Hijacking - https://blog.zolutal.io/two-shot-kernel-shellcode/

Hunting Bugs in Linux Kernel With KASAN: How to Use it & What's the Benefit? - https://slavamoskvin.com/hunting-bugs-in-linux-kernel-with-kasan-how-to-use-it-whats-the-benefit/

Fenomen

w Hydepark

6piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.06.01.md

Here We Go Again: A Five-Bug Chain to Arbitrary APK Install on Samsung S25 - https://bugscale.ch/blog/here-we-go-again-a-five-bug-chain-to-arbitrary-apk-install-on-samsung-s25/

How harnesses and post-training close the open-weight bug-finding gap - https://vincenzoiozzo.com/blog/oss-models-vuln-research

CFITSIO Fuzzing: Memory Corruptions and a Codex-Assisted Pipeline - https://blog.doyensec.com/2026/04/20/cfitsio-fuzzing.html

DirtyCBC: When Linux Kernel Decrypt-Before-MAC Turns Authenticated Encryption Into a Page-Cache Write - https://delphoslabs.com/blog/36142374-e1fe-80a9-9456-d3c64df81bd5/%20linux-rxgk-decrypt-mac

Creating Shadow Copies with VSS API - https://ricardojoserf.github.io/w11shadowcopies/

Autorytet

w Technologia

22piorunów

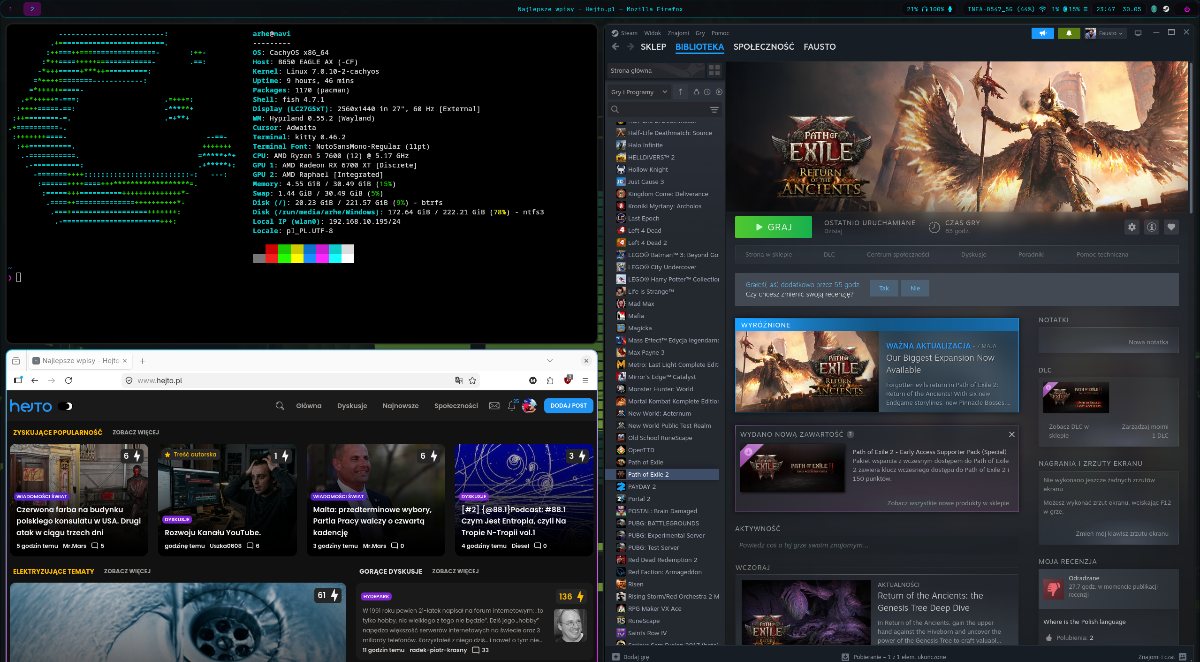
Około dwa tygodnie temu przesiadłem się z windowsa 10 na linuxa i do teraz nie mam potrzeby powrotu. Pierwszy raz używam hyprlanda i poruszanie sie klawiatura oraz łatwość modowania, robią różnice. Jednak nie jest to opcja dla początkujących, bo po uruchomieniu nawet paska startu nie ma ; )

Pokaż więcej komentarzy (12)

Fenomen

w Hydepark

4piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.05.30.md

QEMU abused to evade detection and enable ransomware delivery - https://www.sophos.com/en-us/blog/qemu-abused-to-evade-detection-and-enable-ransomware-delivery

Public disclosure, a response for CVE-2026-33825 patch - https://deadeclipse666.blogspot.com/2026/04/public-disclosure-response-for-cve-2026.html

Operational Workbooks Episode 1: Running a Playbook from a Workbook - https://attackthesoc.com/posts/operational-workbooks-ep1/

CVE-2026-20182: Critical authentication bypass in Cisco Catalyst SD-WAN Controller (FIXED) - https://www.rapid7.com/blog/post/ve-cve-2026-20182-critical-authentication-bypass-cisco-catalyst-sd-wan-controller-fixed/

GURU

w Informatyka

11piorunów

Wymiana dwóch patchcordów + deratyzacja „szafy” + 1,5h

Szybko bo wiedziałem co gdzie na obiekcie jest, znam adresację etc.

Gdybym tam był pierwszy raz to dnia by mi pewnie nie starczyło żeby dojść bez dokumentacji.
Zresztą co widać po stanie gryzonia - też niewcześnie się zorientowali, że coś nie działa..

Na ile wyceniacie taką usługę?

Ile kosztuje taka usługa?

  • 50zł4% (3 głosy)
  • 250zł8% (7 głosów)
  • 500zł15% (13 głosów)
  • 750zł13% (11 głosów)
  • 1000zł20% (17 głosów)
  • Syn mojej koleżanki gra w komputer i by zrobił za darmo33% (28 głosów)
  • optowiadomocoijegomafiatez7% (6 głosów)

85 głosów

Pokaż więcej komentarzy (5)

Zawodowiec

w Programowanie

4piorunów

Jak ograniczyć skutki awarii - circuit breaker - devszczepaniak.pl

W świecie coraz częstszej integracji z LLM-ami i innymi zewnętrznymi usługami ich stabilność staje się realnym problemem architektonicznym. Usługi potrafią być wolne, przeciążone albo niedostępne, co łatwo może przenosić się na naszą aplikację i naszych klientów. Jednym ze

Fenomen

w Hydepark

6piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.05.28.md

Stop Being Weird — Life After Call Stack Spoofing Under CET - https://bigbingus.com/posts/stop-being-weird/

Drupal warns of active exploitation attempts targeting critical SQL injection flaw - https://cyberinsider.com/drupal-warns-of-active-exploitation-attempts-targeting-critical-sql-injection-flaw/

The Hidden Risk of Side-Channel Attacks on Post Quantum Cryptography - https://www.ledger.com/blog-risk-side-channel-attacks-post-quantum-cryptography

RedSun: How Windows Defender's Remediation Became a SYSTEM File Write - https://nefariousplan.com/posts/redsun-windows-defender-system-write

CHECK Removed, Context Confused, Checkmate Achieved - https://starlabs.sg/blog/2026/04-check-removed-context-confused-checkmate-achieved/

Fenomen

w Hydepark

7piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.05.26.md

Revisiting Two-Shot Kernel Shellcode Execution From Control Flow Hijacking https://blog.zolutal.io/two-shot-kernel-shellcode/

Mona, tellme - AI-assisted analysis https://www.corelan.be/index.php/2026/05/14/mona-tellme/

Some notes on the security properties of the pipe_buffer kernel object https://a13xp0p0v.github.io/2026/04/20/pipe-buffer-experiments.html

The Search for AGI through Security: Introducing the World's First AI-Based Novel Attack Vector Researcher https://pwn.ai/blog/the-search-for-agi-through-security-and-novelity

Revisiting Two-Shot Kernel Shellcode Execution From Control Flow Hijacking https://blog.zolutal.io/two-shot-kernel-shellcode

Fenomen

w Hydepark

4piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.05.24.md

An unexpected journey into Microsoft Defender's signature World - https://retooling.io/blog/an-unexpected-journey-into-microsoft-defenders-signature-world

Static Devirtualization of Themida - https://back.engineering/blog/09/05/2026/

The state of Bug Bounty in 2026 - https://aituglo.com/state-of-bug-bounty-in-2026/

Creating Custom x86 Windows Shellcode Using Dynamic API Resolution - https://screetsec.com/blog/custom-x86-windows-shellcode-dynamic-api-resolution

Understanding Integer Overflow in Windows Kernel Exploitation - https://whiteknightlabs.com/2025/05/27/understanding-integer-overflow-in-windows-kernel-exploitation/

Fenomen

w Hydepark

3piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.05.22.md

The QNAP Pattern - https://runiclabs.io/research/qnap-architecture/

Damned OOB - https://ze3tar.github.io/post-zcrx.html

The 429 Microsoft Graph Mystery - https://www.r-tec.net/r-tec-blog-the-429-microsoft-graph-mystery.html

Harness design for long-running application development - https://www.anthropic.com/engineering/harness-design-long-running-apps

GhostTree: Unveiling Path Manipulation Techniques to Bypass Windows Security - https://www.varonis.com/blog/ghosttree-ntfs-trick

Fanatyk

w Hydepark

56piorunów

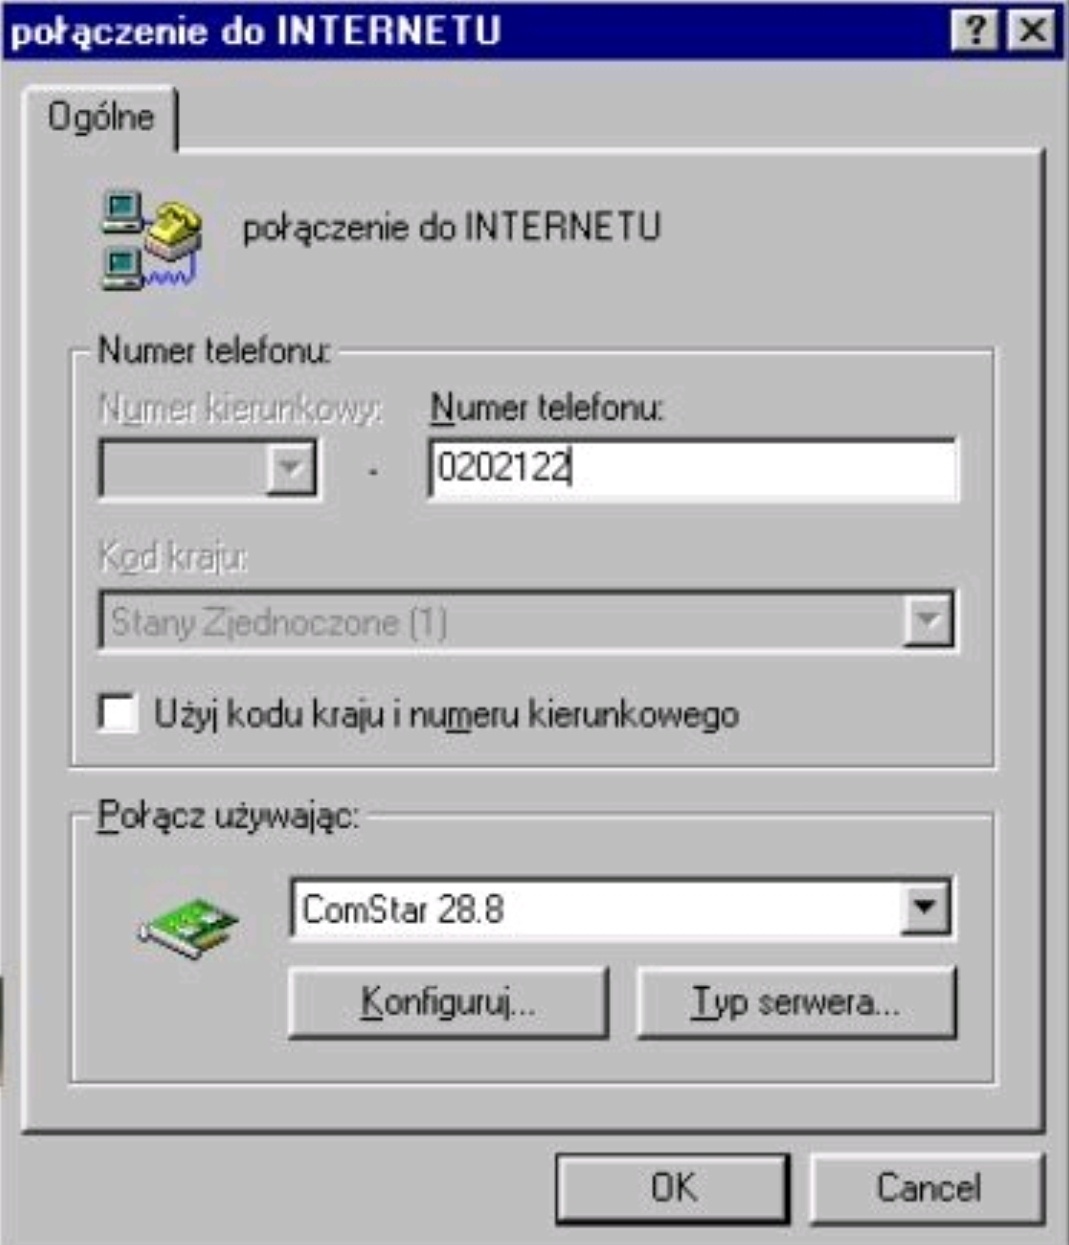
To już równe 30 lat. W maju 1996 udostępniono numer 0202122.

?

Pokaż więcej komentarzy (18)

Fenomen

w Hydepark

4piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.05.20.md

Windows Shell Links in C++: How to Read and Write .lnk Files - https://trainsec.net/library/windows-kernel/windows-shell-links-in-c-how-to-read-and-write-lnk-files/

Where Have All the Complex Windows Malware and Their Analyses Gone? - https://r136a1.dev/2026/05/07/where-have-all-the-complex-malware-and-their-analyses-gone/

CVE-2026-20079 - Cisco FMC Authentication Bypass RCE Analysis - https://www.vulncheck.com/blog/cisco-fmc-auth-bypass-cve-2026-20079

Giving an Agent a Rooted Android Phone - https://workers.io/blog/autonomous-mobile-pentesting/

Ansible Security and Compliance - https://slicker.me/netsec/ansible-security-compliance.html

Fenomen

w Hydepark

7piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.05.18.md

The ServiceNow AI Vulnerability: What Went Wrong and How to Secure Your AI Agents - https://opena2a.org/blogs/servicenow-ai-vulnerability

WinBoat: Drive by Client RCE + Sandbox escape - https://hack.do/posts/winboat-guest-service-host-rce/

After the Takedown: Excavating Abuse Infrastructure with DNS Sinkholes - https://disclosing.observer/2026/01/14/excavating-abuse-infrastructure-dns-sinkholes.html

DLL Sideloading & Proxying for Advance Red Team Engagements - https://www.zerotracelab.com/blog/dll-sideloading

Analysis of Python's .pth files as a persistence mechanism - https://dfir.ch/posts/publish_python_pth_extension/

Fenomen

w Hydepark

4piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.05.16.md

Introduction to Windows shellcode development – Part 1 - https://securitycafe.ro/2015/10/30/introduction-to-windows-shellcode-development-part1/

Reinforcement Learning for Hacking? - https://s1r1us.ninja/posts/reinforcement-learning-for-hacking/

How We Cut LLM Costs by 59% With Prompt Caching - https://projectdiscovery.io/blog/how-we-cut-llm-cost-with-prompt-caching

Instagram account takeover via Meta Pixel script abuse - https://ysamm.com/uncategorized/2026/01/16/leaking-fbevents-ato.html

Automating MS-RPC vulnerability research - https://www.incendium.rocks/posts/Automating-MS-RPC-Vulnerability-Research/

Fenomen

w Hydepark

4piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.05.14.md

CEliteLLM – LiteLLM 1.83.14: Chaining an Environment Variable Leak with Jinja2 SSTI for Remote Code Execution - https://mccaulay.co.uk/rcelitellm-litellm-1-83-14-chaining-an-environment-variable-leak-with-jinja2-ssti-for-remote-code-execution/

Bad Vibes: Comparing the Secure Coding Capabilities of Popular Coding Agents - https://blog.tenzai.com/bad-vibes-comparing-the-secure-coding-capabilities-of-popular-coding-agents/

Drone Hacking Part 1: Dumping Firmware and Bruteforcing ECC - https://neodyme.io/en/blog/drone_hacking_part_1/

Teaching ZFS about time - https://oshogbo.com/blog/86/

Reprompt: The Single-Click Microsoft Copilot Attack that Silently Steals Your Personal Data - https://www.varonis.com/blog/reprompt