Hejto.pl
Dodaj post

Wpisz coś do wyszukania (minimum 2 znaki)

#informatyka

Fenomen

w Hydepark

4piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.05.14.md

CEliteLLM – LiteLLM 1.83.14: Chaining an Environment Variable Leak with Jinja2 SSTI for Remote Code Execution - https://mccaulay.co.uk/rcelitellm-litellm-1-83-14-chaining-an-environment-variable-leak-with-jinja2-ssti-for-remote-code-execution/

Bad Vibes: Comparing the Secure Coding Capabilities of Popular Coding Agents - https://blog.tenzai.com/bad-vibes-comparing-the-secure-coding-capabilities-of-popular-coding-agents/

Drone Hacking Part 1: Dumping Firmware and Bruteforcing ECC - https://neodyme.io/en/blog/drone_hacking_part_1/

Teaching ZFS about time - https://oshogbo.com/blog/86/

Reprompt: The Single-Click Microsoft Copilot Attack that Silently Steals Your Personal Data - https://www.varonis.com/blog/reprompt
Osobistość

w Hydepark

83piorunów

Nastolatek stworzył w domowym warsztacie komputer jednopłytkowy oparty na procesorze AMD Ryzen

Dwa razy oglądałem ten filmik i jestem pod ogromnym wrażeniem. Szkoda, że o takich ludziach mało się słyszy i mało kto ich na początku docenia a do mainstreamu przebijają się opłacane przez tatusiów "naukowycznie". Jak ktoś nie chce oglądać filmiku to jest artykuł na:

Fenomen

w Hydepark

7piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.05.12.md

CSRF Protection without Tokens or Hidden Form Fields - https://blog.miguelgrinberg.com/post/csrf-protection-without-tokens-or-hidden-form-fields

Extending my access: Abusing installed extensions for post compromise - https://futuresight.club/posts/extending-my-access/

exfiltration using numeric-only outputs - https://blog.ikaes.de/exfiltration-using-numeric-only-outputs/

Jenny was a Friend of Mine - MCPs and Friends - https://blog.zsec.uk/bullyingllms/

BACnet-scan - Tool for BACnet/IP and BACnet/SC discovery - https://ricardojoserf.github.io/bacnetscan/

Fenomen

w Hydepark

3piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.05.10.md

CVE-2025-6554: The (rabbit) Hole - https://retr0.zip/blog/cve-2025-6554-the-rabbit-hole.html

EDR Tradecraft: Internals, Detection, Evasion & Advanced Researchg - https://0xdbgman.github.io/posts/edr-internals-research-and-bypass/

WTF Are Abliterated Models? Uncensored LLMs Explained- https://webdecoy.com/blog/wtf-are-abliterated-models-uncensored-llms-explained/

The Claude C Compiler: What It Reveals About the Future of Software - https://www.modular.com/blog/the-claude-c-compiler-what-it-reveals-about-the-future-of-software

First Week, First Hack: Compromising a Package with 40 Million Weekly Downloads - https://www.landh.tech/blog/20260402-img-colour-supply-chain-hack/

Fenomen

w Hydepark

3piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.05.08.md

[Cryptodev-linux] Page-level UAF exploitation - https://nasm.re/posts/cryptodev-linux-vuln/

[Research] LLVM based VMProtect Devirtualization: Part 1 (EN) - https://hackyboiz.github.io/2025/09/11/banda/LLVM_based_VMP/en/

Fuzzing to Zero-Day: Pwning V8CTF With TurboFan Type Confusion, CVE-2025-2135 - https://www.zellic.io/blog/pwning-v8ctf/

Shadow SSDT Hijacking: Achieving Kernel Code Execution via Read-Write Primitives - https://www.exploitpack.com/blogs/news/shadow-ssdt-hijacking-to-achieve-kernel-code-execution-via-rw-primitives

ImageMagick: From Arbitrary File Read to File Write In Every Policy - https://pwn.ai/blog/imagemagick-from-arbitrary-file-read-to-rce-in-every-policy-zeroday

Fenomen

w Hydepark

7piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.05.06.md

How a single typo led to RCE in Firefox - https://kqx.io/post/firefox0day/

How I make CTF challenges harder to solve with AI - https://danisy-eisyraf-portfolio.super.site/blog-posts/how-i-make-ctf-challenges-harder-to-solve-with-ai

The Cost of Understanding: LLM-Driven Reverse Engineering vs Iterative LLM Obfuscation - https://www.elastic.co/security-labs/llm-reversing-vs-llm-obfuscation

N-Day Research with AI: Using Ollama and n8n - https://ghostbyt3.github.io/blog/nday-research-ai

gdrv3.sys - Reverse Engineering a Signed Kernel Driver with 13 Hardware Access Primitives - https://zonifer.dev/posts/byovd-kernel-driver-hardware-primitives.html

Gruba ryba

w LINUX

8piorunów

Inicjatywa systemdfree.com - GNU/Linux nie musi oznaczać jednego obowiązkowego initu

Stronka pokazująca korzyści z wykorzystania alternatywnych, do systemd initów. Takie plusy jak prostota, niski narzut czy większa transparentność. Plus oczywiście baza dystrybucji #linux #init #systemd #technologia #informatyka #systemyoperacyjne

Fenomen

w Hydepark

2piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.05.04.md

Bug bounty is the future of CTF...? - https://blog.krauq.com/post/bug-bounty-is-the-future-of-ctf

CVE-2026-21876: Critical Multipart Charset Bypass Fixed in CRS 4.22.0 and 3.3.8 - https://coreruleset.org/20260106/cve-2026-21876-critical-multipart-charset-bypass-fixed-in-crs-4.22.0-and-3.3.8/

WhatsApp Signal Privacy Vulnerability: Silent Tracking Attack Exposed (2026) - https://baizaar.tools/whatsapp-signal-privacy-vulnerability-attack-2026/

MongoBleed: CVE-2025-14847 Memory Corruption in MongoDB. Your Database Talks Back - https://phoenix.security/mongobleed-vulnerability-cve-2025-14847/

Claude Magic String Denial of Service - https://hackingthe.cloud/ai-llm/exploitation/claude_magic_string_denial_of_service/

Fenomen

w Hydepark

3piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.05.02.md

Introducing MCP-Scan: Protecting MCP with Invariant https://invariantlabs.ai/blog/introducing-mcp-scan

Thinking in Graphs with IPAHound https://swarm.ptsecurity.com/thinking-in-graphs-with-ipahound/

A brief analysis of a vulnerability in the glibc (CVE-2025-4802) https://allelesecurity.com/libc-vuln-analysis/

Digital Forensics: Basic Linux Analysis After Data Exfiltration https://hackers-arise.com/digital-forensics-basic-linux-analysis-after-data-exfiltration/

Hooked on Linux: Rootkit Taxonomy, Hooking Techniques and Tradecraft https://www.elastic.co/security-labs/linux-rootkits-1-hooked-on-linux

Fenomen

w Hydepark

5piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.04.30.md

Malware Development Essentials for Operators - https://f00crew.org/0x33

Reverse engineering my cloud-connected e-scooter and finding the master key to unlock all scooters - https://blog.nns.ee/2026/01/06/aike-ble/

DLL Sideloading & Proxying for Advance Red Team Engagements - https://www.zerotracelab.com/blog/dll-sideloading

From KernelSnitch to Practical msg_msg/pipe_buffer Heap KASLR Leaks - https://lukasmaar.github.io/posts/heap-kaslr-leak/index.html

Automating the Operator: Integrating LLMs into Offensive Security Workflows - https://www.armadin.com/blog-posts/automating-the-operator-integrating-llms-into-offensive-security-workflow

Fenomen

w Hydepark

5piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.04.28.md

C2 Redirectors: Advanced Infrastructure for Modern Red Team Operations - https://xbz0n.sh/blog/c2-redirectors

When WebSockets Lead to RCE in CurseForge - https://elliott.diy/blog/curseforge/

Finding Gadgets Like it’s 2026 - https://www.atredis.com/blog/2026/3/12/findings-gadgets-like-its-2026

Learn Something Old Every Day, Part XX: 8087 Emulation on 8086 Systems - https://www.os2museum.com/wp/learn-something-old-every-day-part-xx-8087-emulation-on-8086-systems/

It's Not Always DNS: Exploring How Name Resolution Works - https://cefboud.com/posts/dns-name-resolution-deep-dive-internals/

Gruba ryba

w Hydepark

8piorunów

Podstawowe obowiązki podmiotów kluczowych i ważnych wynikające z unijnej dyrektywy NIS2 / ustawy KSC 2.0.

Zarządzasz siecią komputerową, serwerami, danymi w firmie która wpadła na listę NIS2 / KSC? Coś dla Ciebie.

Zapraszam do lektury:

https://czasopismo.legeartis.org/2026/04/nis2-obowiazki-podmiotow-kluczowych-waznych-krajowy-system-cyberbezpieczenstwa/

Fenomen

w Hydepark

4piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.04.26.md

Some notes on the security properties of the pipe_buffer kernel object - https://a13xp0p0v.github.io/2026/04/20/pipe-buffer-experiments.html

Petlibro: Your Pet Feeder Is Feeding Data To Anyone Who Asks - https://bobdahacker.com/blog/petlibro

Prepared Statements? Prepared to Be Vulnerable - https://blog.mantrainfosec.com/blog/18/prepared-statements-prepared-to-be-vulnerable

Evading Elastic EDR's call stack signatures with call gadgets - https://offsec.almond.consulting/evading-elastic-callstack-signatures.html

Every minute you aren't running 69 agents, you are falling behind - https://geohot.github.io//blog/jekyll/update/2026/03/11/running-69-agents.html

Fenomen

w Hydepark

8piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.04.24.md

Needle in the haystack: LLMs for vulnerability research - https://devansh.bearblog.dev/needle-in-the-haystack/

Detecting Vision-Based AI Agents: Operator and Beyond - https://webdecoy.com/blog/detecting-vision-based-ai-agents-operator-computer-use/

Astral Projection: Advanced Module Stomping - https://kuwaitist.github.io/posts/Astral-Projection/

Now You See mi: Now You're Pwned - https://labs.taszk.io/articles/post/nowyouseemi/

Jenny was a Friend of Mine - MCPs and Friends - https://blog.zsec.uk/bullyingllms/

Gruba ryba

w Cybersecurity

17piorunów

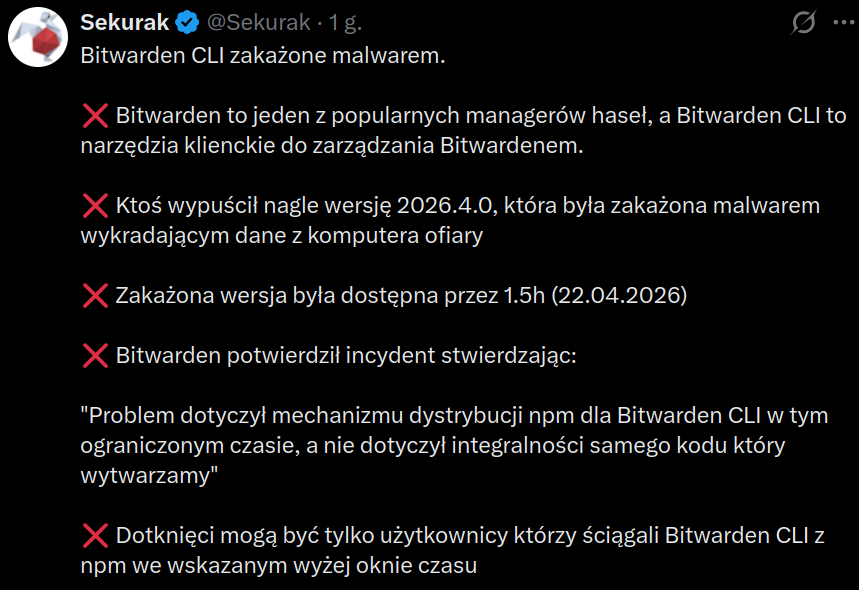
Bitwarden zhakowany!

Problem tyczy się TYLKO Bitwarden CLI (zarządzanie z konsoli).

Na chwilę obecną nie ma informacji aby inne wersje (okienkowe) były zainfekowane.

Złośliwa paczka była dostępna "tylko" przez 1,5 godziny.

GURU7piorunów

@Marchew nosz k⁎⁎wa, najpierw lastpass a teraz Bitwarden. Gdzie mam się przenieść teraz?

Gruba ryba7piorunów

@Endrevoir Nie jestem ekspertem.

Ale dla mnie keepass i keepass XC.

Offline daje mi pozorne bezpieczeństwo.

Ale tez managery offline to w większości target domowy. Cyberuchy pchają się tam gdzie korpo, a więc i rozwiązania online + synchronizacja pomiędzy urządzeniami.

Pokaż więcej komentarzy (5)

Fenomen

w Hydepark

6piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.04.22.md

How I Reverse Engineered a Rust Botnet and Built a C2 Honeypot to Monitor Its Targets - https://beelzebub.ai/blog/rust-ddos-botnet-honeypot-c2-decoding/

When OAuth Becomes a Weapon: Lessons from CVE-2025-6514 - https://amlalabs.com/blog/oauth-cve-2025-6514/

Replaced by a Goldfish - https://clawd.it/posts/10-replaced-by-a-goldfish/

(CVE-2025-47985) Windows Event Tracing Insufficient Validation Leading to Elevation of Privilege - https://starlabs.sg/advisories/25/25-47985/

AWS Penetration Testing Guide: Techniques & Methodology - https://deepstrike.io/blog/aws-penetration-testing-guide-techniques-and-methodology

Fenomen

w Hydepark

5piorunów

ink on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.04.20.md

Turning a Chinese IoT camera into an owl livestream - https://blog.alexbeals.com/posts/owl-cam

Microsoft Brokering File System Elevation of Privilege Vulnerability - https://www.pixiepointsecurity.com/blog/nday-cve-2025-29970/

Improving the stealthiness of memory injections techniques - https://naksyn.com/edr%20evasion/2023/06/01/improving-the-stealthiness-of-memory-injections.html

Vulnhalla: Picking the true vulnerabilities from the CodeQL haystack - https://www.cyberark.com/resources/threat-research-blog/vulnhalla-picking-the-true-vulnerabilities-from-the-codeql-haystack

DSCourier: Weaponizing DSC via WinGet COM API for Evasive Execution - https://eclipsesec.com/posts/DSCourier/

Zawodowiec

w AI

5piorunów

Worktree w pracy z Claude Code - devszczepaniak.pl

Claude Code potrafi znacząco przyspieszyć pracę. Jednak jego prawdziwy potencjał widać wtedy, gdy nauczysz się wykorzystywać go równolegle do kilku zadań jednocześnie.\ \ W najnowszym artykule na blogu omawiam mechanizm worktree w Gicie. Dowiesz się, jak wykorzystać go w pracy z Claude