Hejto.pl
Dodaj post

Wpisz coś do wyszukania (minimum 2 znaki)

#informatyka

Zawodowiec

w Programowanie

5piorunów

Dlaczego NIE warto delegować kodowania agentom AI - devszczepaniak.pl

Delegowanie pisania kodu do AI ma ogrom zalet. W ciągu ostatnich dwóch lat, za sprawą narzędzi AI, wyprodukowałem wielokrotnie więcej kodu niż kiedykolwiek wcześniej. Przez ten czas zacząłem jednak dostrzegać sporo istotnych wad tego podejścia. O tym, jakie problemy dostrzegam w tym
Fenomen

w Hydepark

4piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.08.04.md

Miasma npm Supply Chain Attack: Self-Spreading Worm via Phantom Gyp - https://www.stepsecurity.io/blog/binding-gyp-npm-supply-chain-attack-spreads-like-worm

ToolUsed: nRF Connect - https://darkmentor.com/bt.html

KindaRails2Shell: How a MATLAB file reads your secrets and pops a shell on Rails - https://ethiack.com/info-hub/research/kindarails2shell-how-a-matlab-file-reads-your-secrets-and-pops-a-shell-on-ruby-on-rails

Who Runs Cl0p? Inside the Most Elusive Ransomware Operation in the World - https://rmoskovy.github.io/posts/who-runs-clop-ransomware-investigation/

Microsoft's Project Silica - https://blog.dshr.org/2026/07/microsofts-project-silica.html

Fenomen

w Hydepark

2piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.08.02.md

SakDriver: Reversing a Kernel Driver Rootkit - https://0xsec.gitbook.io/0xsec/malware-analysis/sakdriver-reversing-a-kernel-driver-rootkit

GAP - Ghost Anchor Persistence: Fileless Extension Persistence in Chromium Browsers - https://fir3n0x.github.io/posts/GAP-Ghost-Anchor-Persistence-Fileless-Extension-Persistence-in-Chromium-Browsers/

IonStack part II: GhostLock, a stack-UAF that has existed in ALL Linux distributions for 15 years - https://nebusec.ai/research/ionstack-part-2/

Turning Chrome Remote Desktop into Pure Red Team Ops - https://zerotracelab.com/blog/chrome-remote-desktop-red-ops

CVE-2026-40369: Twelve Bytes to Escape the Browser Sandbox - https://voidsec.com/cve-2026-40369-browser-sandbox-escape/

Fenomen

w Hydepark

4piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.07.31.md

Golang code review notes II - https://www.elttam.com/blog/golang-code-review-notes-ii

Now You See mi: Now You're Pwned - https://labs.taszk.io/articles/post/nowyouseemi/

ESC8s and Where to Find Them - https://www.abdulmhsblog.com/posts/esc8andfindingwebenrollmentendpoints/

1-Click GitHub Token Stealing via a VSCode Bug - https://blog.ammaraskar.com/github-token-stealing/

Introducing VulHunt: A High-Level Look at Binary Vulnerability Detection - https://www.binarly.io/blog/introducing-vulhunt-a-high-level-look-at-binary-vulnerability-detection

Fenomen

w Hydepark

4piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.07.29.md

Defeating Windows DEP Using ROP Chains Leveraging VirtualAlloc - https://screetsec.com/blog/defeating-windows-dep-using-rop-chains-leveraging-virtualalloc

A Shell Is Worth a Thousand Images: Bing Images RCEs - https://xbow.com/blog/bing-images-rce-vulnerabilities

One of the many flaws of Phi untagging: CVE-2026-4447 - https://kqx.io/post/cve-2026-4447/

AI Assisted Vulnerability Research on Embedded Targets - https://quentinkaiser.be/security/2026/07/18/ia-assisted-vuln-research/

Race Against The Patch: The Evolution of Four Exploit Chains in LiteLLM - https://starlabs.sg/blog/2026/05-race-against-the-patch-the-evolution-of-four-exploit-chains-in-litellm/

Fenomen

w Hydepark

6piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.07.27.md

The Gold Mine Red Teamers Never Touch - https://www.abdulmhsblog.com/posts/useingthewindowssourcecode/

How harnesses and post-training close the open-weight bug-finding gap - https://vincenzoiozzo.com/blog/oss-models-vuln-research

Fit for Detection: Hunting U-Boot Vulnerabilities at Scale - https://www.binarly.io/blog/hunting-u-boot-at-scale

AI-Assisted Fuzzing: Generating Harnesses with a Local LLM - https://www.8ksec.io/ai-assisted-fuzzing-harness-local-llm/

Privilege Escalation via a Page Use-After-Free in Qualcomm's AI Accelerator Linux Kernel Driver - https://lukasmaar.github.io/posts/qaic-page-uaf/index.html

Fenomen

w Hydepark

4piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.07.25.md

Vulnerabilities of Realtek SD card reader driver, part 1 - https://zwclose.github.io/2024/10/14/rtsper1.html

How to Save Millions by Self-Hosting LLMs - https://cline.bot/blog/how-to-save-millions-by-self-hosting-llms

Pop a Calc: The Crystal Palace Way - https://kerekesha.com/blog/pop-a-calc-the-crystal-palace-way

GhostTree: Unveiling Path Manipulation Techniques to Bypass Windows Security - https://www.varonis.com/blog/ghosttree-ntfs-trick

Advanced Module Stomping & Heap/Stack Encryption - https://labs.cognisys.group/posts/Advanced-Module-Stomping-and-Heap-Stack-Encryption/

Statysta

w LINUX

4piorunów

_Robię rzeczy z Linuxem i nie formatuję od razu_

Hej. Zajmuję się naprawą oprogramowania — głównie Linux, Steam Deck, też Windows jak trzeba. Systemy po aktualizacjach, konflikty, uszkodzone partycje, problemy z uruchamianiem.

Pracuję zdalnie albo stacjonarnie w Szczecinie. Podłączam się, troubleshootuję, naprawiam. Nie formatuję od razu — naprawiam.

Jak ktoś ma problem z Linuxem i nie wie co zrobić — pisz. Jak nie będę mógł pomóc, powiem szczerze. Bez ściemy.

WhatsApp: 508 302 053

Pokaż więcej komentarzy (19)

Fenomen

w Hydepark

3piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.07.23.md

How I Found Open-Source 0-days with an LLM Multi-Agent Workflow - https://blog.cykor.kr/2026/02/How-I-Found-Open-Source-0-days-with-an-LLM-Multi-Agent-Workflow

Building an AI-Based Vulnerability Detection Workflow - https://se1en.tistory.com/16

Mapping Virtual to Physical Addresses Using Superfetch - https://www.outflank.nl/blog/2023/12/14/mapping-virtual-to-physical-adresses-using-superfetch/

GDID: The Windows Global Device Identifier - https://zerotracelab.com/blog/gdid-windows-tracking

C111000: Race Against The Virtual Machine or how a SUID binary in VMware Fusion was raced to gain root privileges on macOS - https://therealcoiffeur.com/c111000.html

Fenomen

w Hydepark

4piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.07.21.md

Hijacking the Windows "MareBackup" Scheduled Task for Privilege Escalation - https://itm4n.github.io/hijacking-the-windows-marebackup-scheduled-task-for-privilege-escalation/

oad balancing usage across multiple codex accounts - https://pepsipu.com/blog/2026-04-agent-scheduling/

TAPOcalypse Now: Exploiting TP-Link Smart Devices From Anywhere - https://labs.taszk.io/articles/post/tapocalypse/

In-depth Windows Telemetry - https://blog.otterpwn.com/research/In-depth-Windows-Telemetry

When Defenses Become Attack Surface: CVE-2026-20971, a Samsung Kernel UAF - https://lucidbitlabs.com/blog/when-defenses-become-attack-surface/

Zawodowiec

w Programowanie

4piorunów

EventCatalog - SKUTECZNA dokumentacja architektury Twojego systemu - devszczepaniak.pl

EventCatalog to narzędzie do dokumentowania architektury systemów w podejściu Documentation as Code. Pozwala opisywać zdarzenia, komendy, usługi, domeny i przepływy między nimi. Dzięki temu wiedza o architekturze trzymana jest blisko kodu i jest łatwiejsza w utrzymaniu.\ \ W najnowszym

Fenomen

w Hydepark

3piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.07.19.md

I handed the epoll UAF to an agent - https://guysrd.github.io/epoll-uaf-agent

AI-FI: Giving Claude Code Glitch Skills for Bypassing Secure Boot - https://raelize.com/blog/ai-fi-giving-claude-code-glitch-skills-for-bypassing-secure-boot/

Patterns for Building Cybersecurity Evals - https://eugeneyan.com/writing/cybersecurity-evals/

BingusLdr: CET Compatible Stack Spoofing - https://bigbingus.com/posts/bingusldr-cet-stack-spoofing/

Keys to the Kingdom: Anonymous SQL Injection in Drupal Core (CVE-2026-9082) - https://slcyber.io/research-center/keys-to-the-kingdom-anonymous-sql-injection-in-drupal-core-cve-2026-9082

Fenomen

w Hydepark

3piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.07.17.md

Dan Guido - 200 Bugs/Week/Engineer: How We Rebuilt Trail of Bits Around AI | [un]prompted 2026 - https://www.youtube.com/watch?v=kgwvAyF7qsA

Privilege Escalation via a Page Use-After-Free in Qualcomm's AI Accelerator Linux Kernel Driver - https://lukasmaar.github.io/posts/qaic-page-uaf/index.html

Lost in relocation: analysis of a new loader distributing CASTLESTEALER - https://www.elastic.co/security-labs/oxloader-malware-loader-infostealer

AI-FI: Reproducing adb to root on Google's TV Streamer using Claude in less than 15 minutes - https://raelize.com/blog/ai-fi-reproducing-adb-to-root-on-googles-tv-streamer-using-claude/

futex: remove_waiter stack uaf - https://guysrd.github.io/rtmutex

Fenomen

w Hydepark

8piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.07.15.md

Megalodon: Mass GitHub Repo Backdooring via CI Workflows - https://safedep.io/megalodon-mass-github-repo-backdooring-ci-workflows/

Mapping Virtual to Physical Addresses Using Superfetch - https://www.outflank.nl/blog/2023/12/14/mapping-virtual-to-physical-adresses-using-superfetch/

Accelerating EDR Evasion with LLM-Driven Analysis - https://specterops.io/blog/2026/06/29/llm-powered-edr-analysis/

Carbonara: The MediaTek exploit nobody served - https://itssho.my/blog/article/serving-carbonara

DoublePulsar: A User-Defined Reflective Loader in the Crystal Palace and Tradecraft Garden Era - https://memn0ps.github.io/doublepulsar-a-user-defined-reflective-loader-in-the-crystal-palace-and-tradecraft-garden-era/

Fenomen

w Hydepark

8piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.07.13.md

klist.exe Revisited: Internals and Further Use Cases - https://jakeotte.com/posts/klist-revisited.html

Playing a Different Game: Rethinking Modern Defense Evasion - https://c0rnbread.com/playing-a-different-game-rethinking-modern-defense-evasion/

Inferring Network Protocols from Traffic with MARISSA - https://reversea.me/index.php/inferring-network-protocols-from-traffic-with-marissa/

Rusty Bootkit - Windows UEFI Bootkit in Rust (Codename: RedLotus) - https://memn0ps.github.io/rusty-windows-uefi-bootkit/

Offensive PowerShell for Red Teamer with Defense Evasion Techniques - https://screetsec.com/blog/offensive-powershell-for-red-teamer-with-defense-evastion-techniques

Fenomen

w Hydepark

3piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.07.11.md

MSFDefender: Metasploit Windows Modules Detonation & Analysis -mhttps://bloo.io/blog/msfdefender-metasploit-windows-modules-detonation-analysis

Studying LLM Workflows Until They Actually Find Cool Bugs - https://felixbillieres.github.io/posts/llm-bug-bounty-pipeline-2026/

Becoming the Machine, A Virtual Account's Guide to Total Control - https://www.abdulmhsblog.com/posts/iammachine/

Hack the Elephant One Bite at a Time: NUL byte SQL Injection in pdo_firebird and NULL Pointer Dereference in PDO via pdo_pgsql - https://swarm.ptsecurity.com/hack-the-elephant-one-bite-at-a-time-nul-byte-sql-injection-in-pdo_firebird-and-null-pointer-dereference-in-pdo-pgsql/

Discovery & Validation in the Linux Kernel (Part 3): Local vs Frontier Models h- ttps://bynar.io/blog/discovery-validation-in-the-linux-kernel-part-3-local-vs-frontier-models

Gruba ryba

w Wiadomości Polska

10piorunów

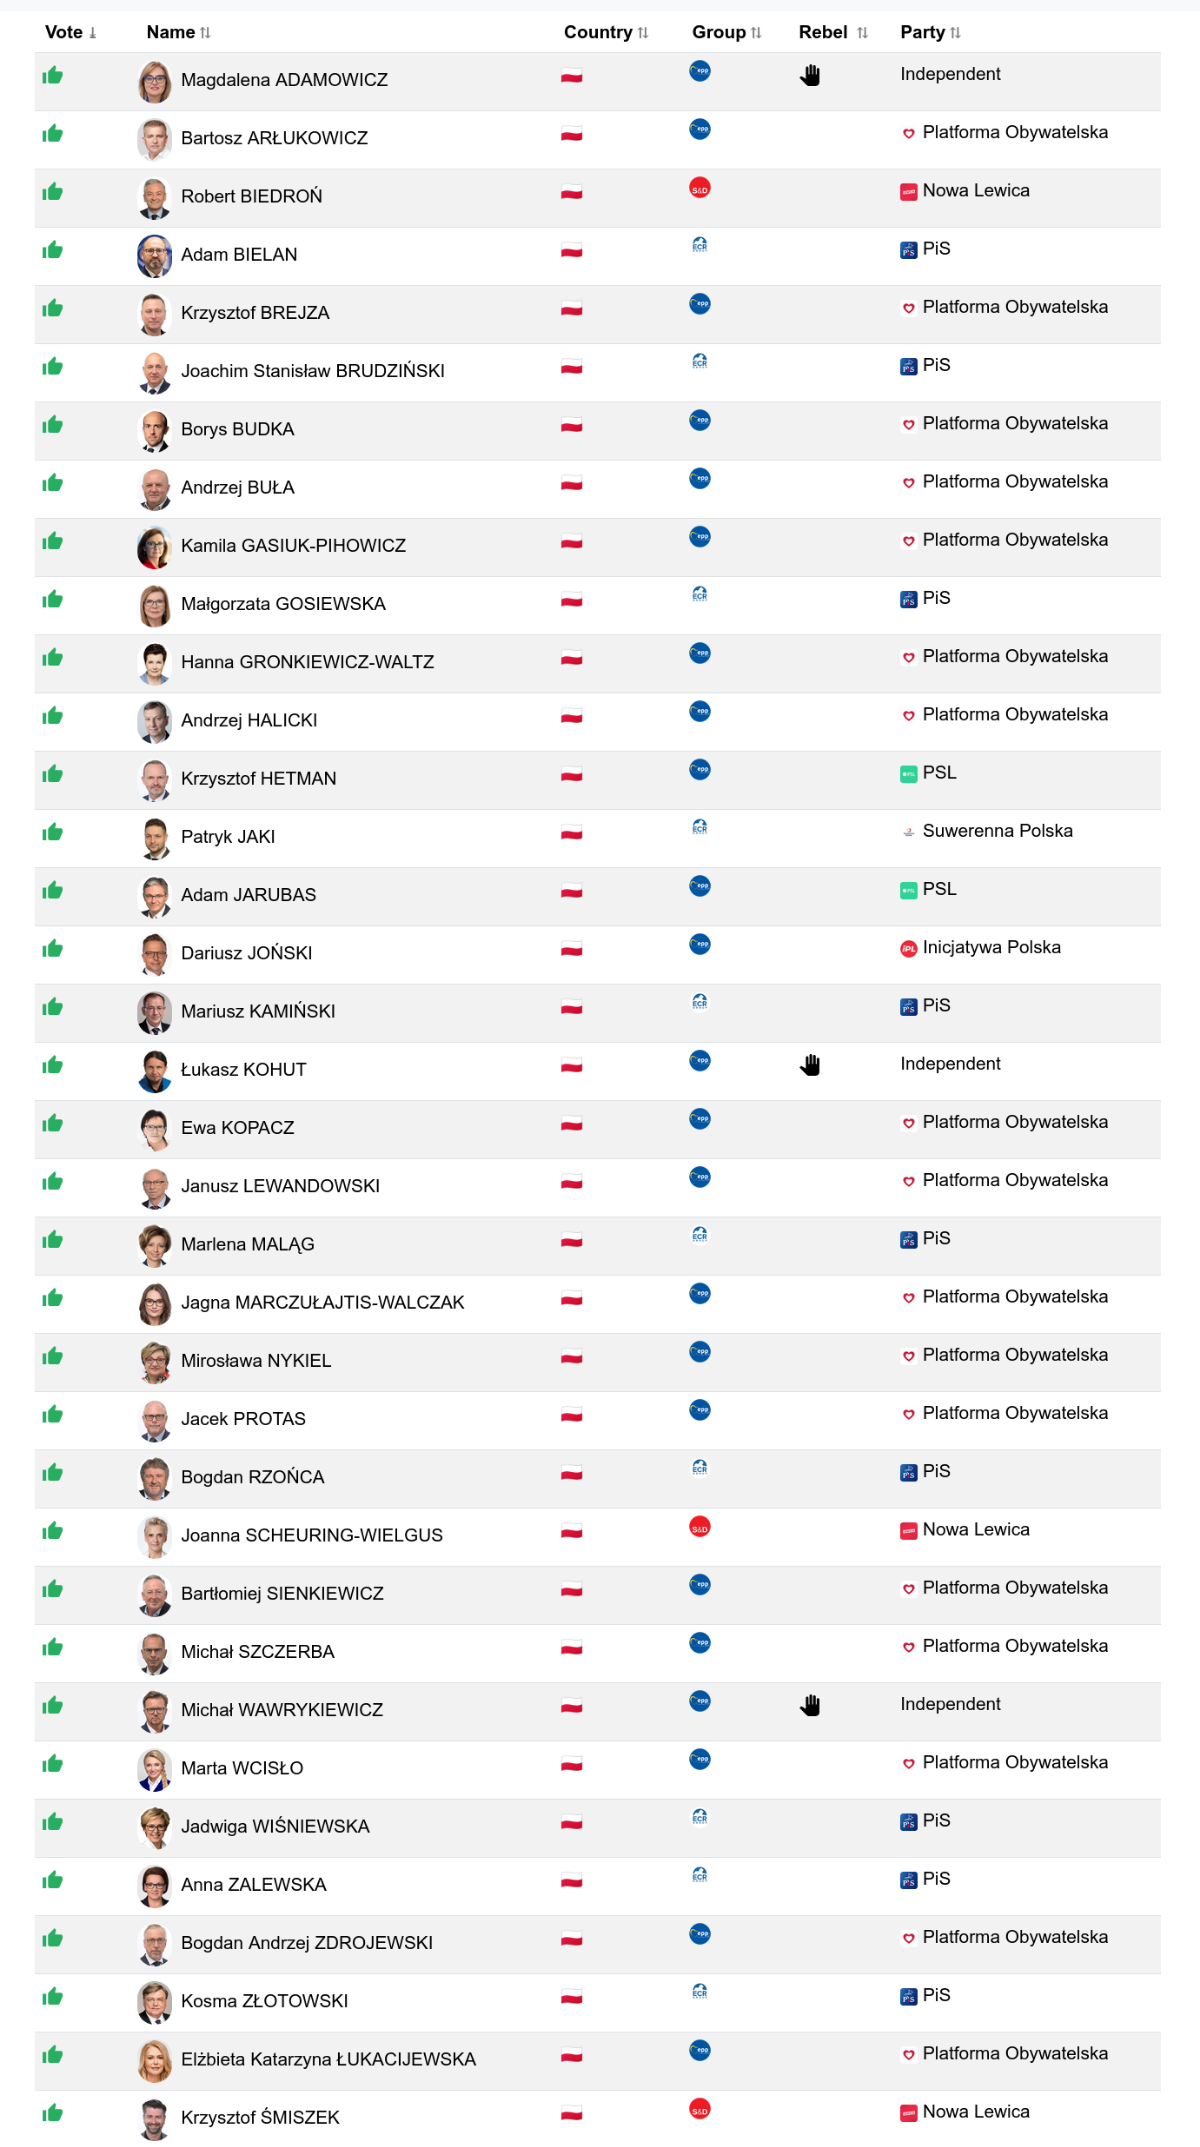
Chat Control 1.0 przyjęty przez Parlament Europejski tylnymi drzwiami

https://pl.euronews.com/next/2026/07/10/chat-control-10-przyjety-przez-parlament-europejski-tylnymi-drzwiami

Oczywiście jak zwykle opakowane jest to w "dobro dzieci".

A to lista europosłów głosująca za skanowaniem prywatnych wiadomości w komunikatorach:

Gruba ryba2piorunów

Jakby co to tu głosy odmienne (jeśli chcecie wiedzieć na kogo ewentualnie głosowac w następnych eurowyborach):

Pokaż więcej komentarzy (8)

Fenomen

w Hydepark

2piorunów

Link on Github --> https://github.com/Nieuport/news-and-links/blob/gh-pages/docs/2026.07.09.md

Breaking eBPF Security: How Kernel Rootkits Blind Observability Tools - https://matheuzsecurity.github.io/hacking/ebpf-security-tools-hacking/

TAPOcalypse Now: Exploiting TP-Link Smart Devices From Anywhere - https://labs.taszk.io/articles/post/tapocalypse/

Leanstral 1.5: Proof Abundance for All https://mistral.ai/news/leanstral-1-5/

CVE-2025-38352 (Part 1) - In-the-wild Android Kernel Vulnerability Analysis + PoC - https://faith2dxy.xyz/2025-12-22/cve_2025_38352_analysis/

Hunting Sleeping Giants: Detecting Encrypted Beacon Sleep Obfuscation - https://justruss.tech/index.php/2026/06/21/hunting-sleeping-giants-detecting-encrypted-beacon-sleep-obfuscation/